PRODUCT / SAVA EDR
Detection and response on the endpoint.
SAVA EDR collects events on the endpoint, finds suspicious chains by behavior and lets you respond from a central console.
Short answers
What is EDR?
EDR (Endpoint Detection & Response) is a security approach that monitors process, file and network events on endpoints such as computers and servers, detects suspicious behavior and lets you respond to incidents. SAVA EDR is a Turkish-built product of this kind.
What is endpoint security?
Endpoint security is the set of measures that protect devices such as computers and servers from threats. EDR provides the detection and response layer within it.
What is the difference between EDR and antivirus?
Antivirus traditionally focuses on blocking known malware. EDR monitors events, finds suspicious behavior chains, keeps an incident record and provides response. Which one you need depends on your environment; write to us for details.
What does “Turkish EDR” mean?
A Turkish (yerli) EDR is an EDR product developed in Türkiye. SAVA EDR is developed in Türkiye by SAVA Cybersecurity, with support in Turkish. This is not a claim of any certificate or official status.
The path of an incident
- 01
Collect
Process, file and network events are collected continuously from the endpoint.
- 02
Analyze
Collected data is evaluated for suspicious behavior.
- 03
Alert
Alerts are generated and prioritized by severity.
- 04
Respond
The process is terminated, the file quarantined, the host isolated.
CONSOLE
Console
The modules where security operations come together.
DASHBOARD
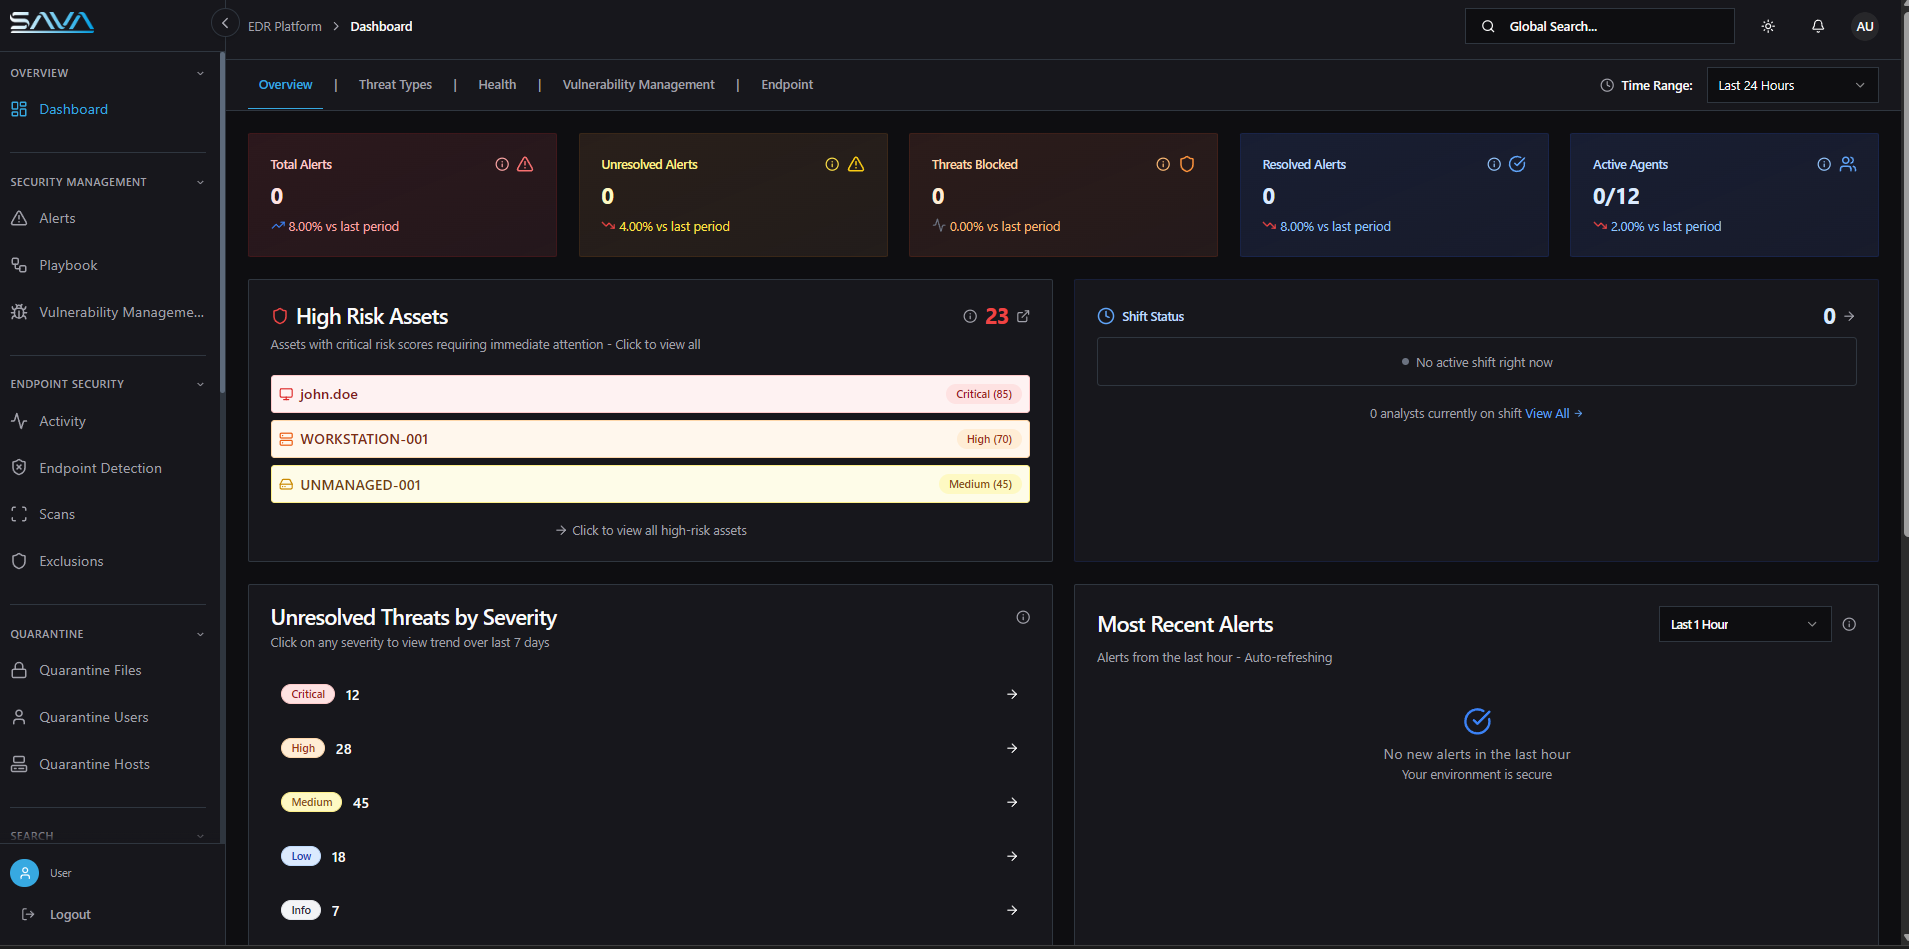
Overview
Alerts, high-risk assets and a threat summary on one screen.
ALERTS
Alerts
Prioritized alerts; unresolved threats by severity.
PLAYBOOK
Playbook
Manage response steps with playbooks.
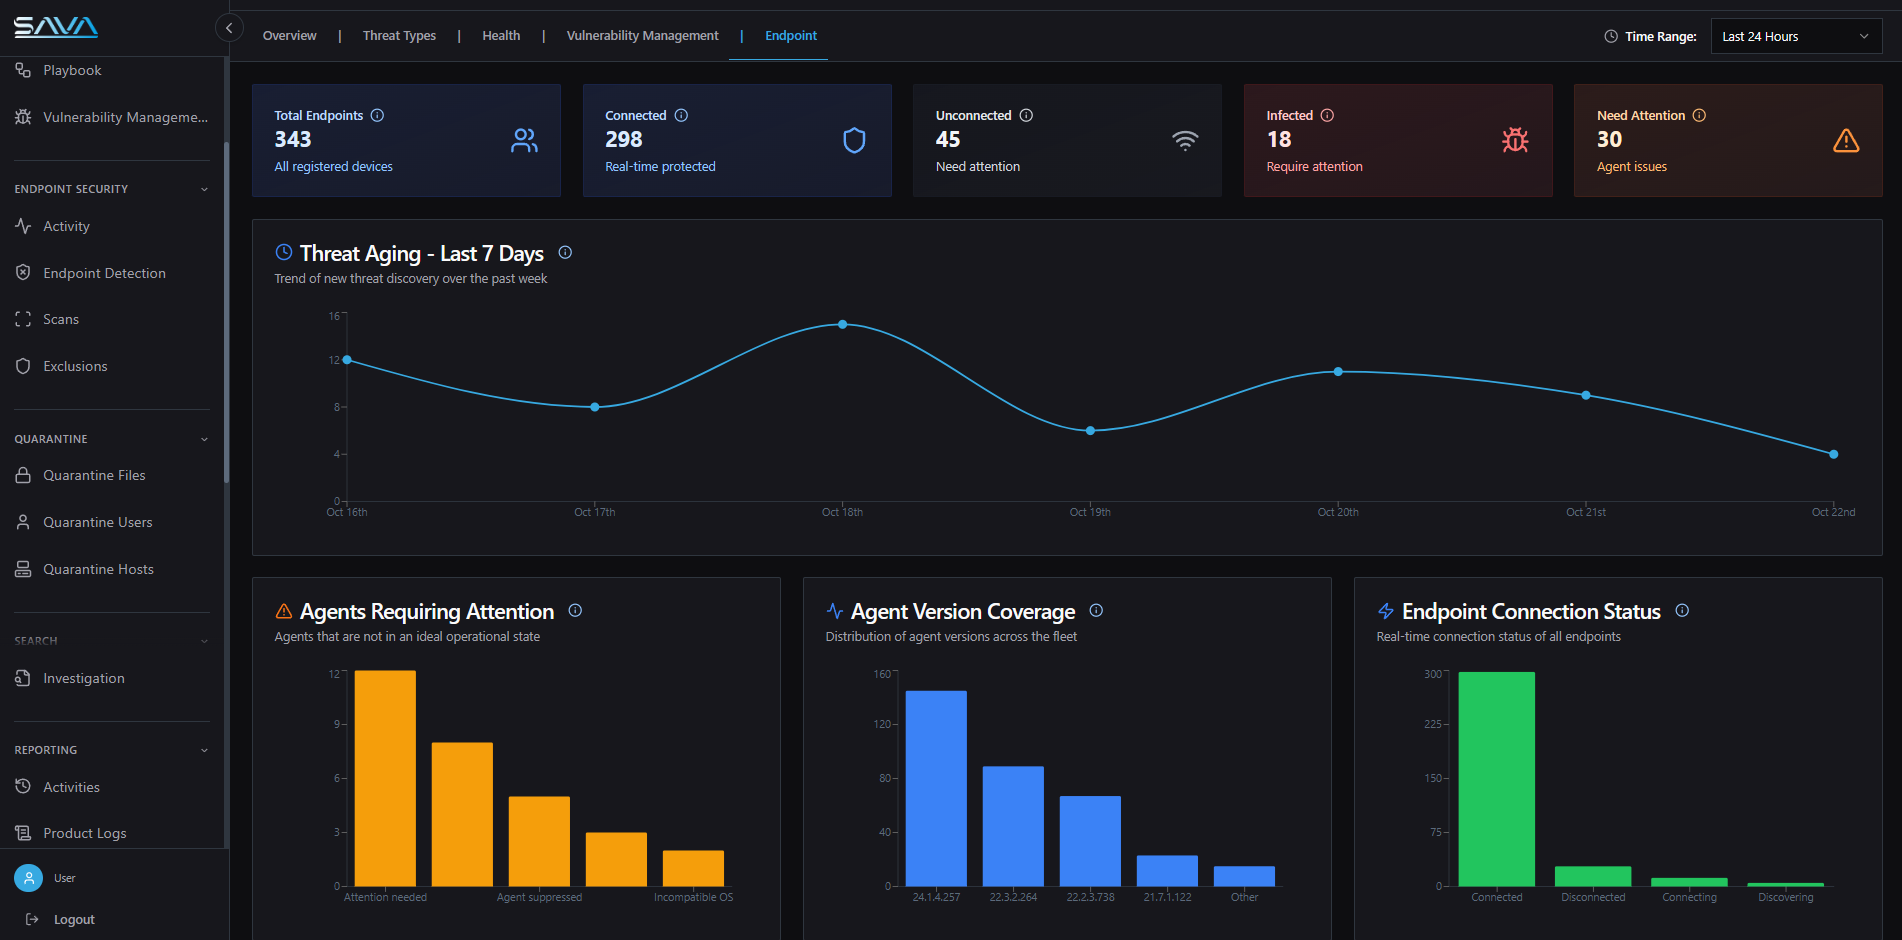
ENDPOINT
Endpoint detection
Follow activity and detections per endpoint.
SCANS
Scans
See scans on endpoints and their results.
EXCLUSIONS
Exclusions
Manage items left out of detection.
QUARANTINE
Quarantine
Manage file, user and host quarantine in one place.
VULNERABILITY
Vulnerability management
List CVEs by severity and affected systems.
INVESTIGATION
Investigation
Investigate an incident with its timeline and affected host.
REPORTS
Reports
Reports on security events and system status.
From the console
DEPLOYMENT
Where does it run?
Operating system support and deployment models.
Supported operating systems
- Windows
- Linux
- macOS
Support scope varies by version. Write to us for the current list.
Deployment models
- On-premises
- Private cloud
- Hybrid
See it in your environment.
In a short demo we show what SAVA EDR sees on your endpoint and what it responds to.